Crayonic Badge™
Specification of Version B3 & B4 & B5
© Crayonic B.V.
Version B3 & B4 & B5
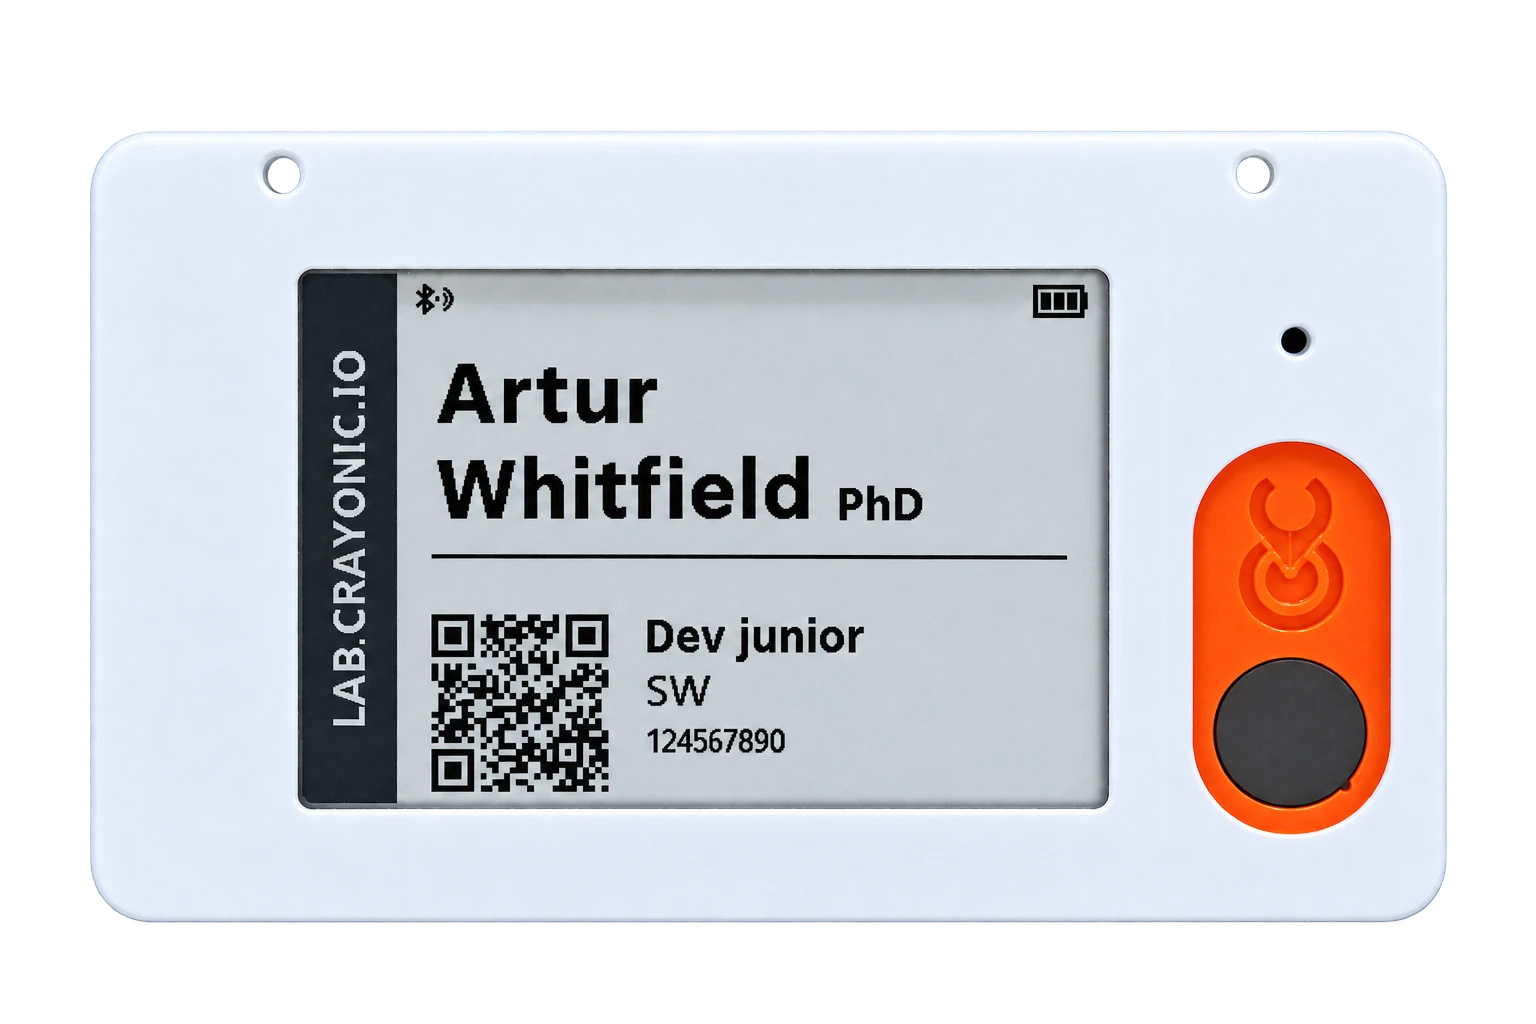
Legacy versions B1 and B2 (not sold anymore)

Passwordless Access & Identity Wallet
Crayonic Badge™ (CB) is a smart wearable device in a badge holder form factor for securing digital transactions in online and offline environments. CB implements multiple open standards with well-defined protocols and enables highly secure identification and authentication of its owner across a range of use cases.
The Badge secures all sensitive personal information such as biometric templates, cryptographic keys, FIDO2 credentials, legacy passwords, and X.509 certificates. With this data, users can interact with various devices and applications - from logical access to desktop PCs, mobile devices, and IoT to cloud applications and even physical access systems.
Where this fits
The Badge is the hardware wallet the user wears; see Solution Architecture for how it connects to the Bridge, Agent, CCM/CDM, the Secure Audio Service and the RTLS/Comms services.
The Badge can augment existing PKI or physical access proximity card infrastructure by accepting legacy smart cards with RFID and/or physical contact interfaces. This can speed up and further secure their usage.
Multiple Authentication Factors On-Device
Identification and authentication of the user are based on knowledge and biometric factors, thus meeting the triple factor authentication criteria for even the highest security use cases - possession, knowledge, and inherence. All Badge versions support static biometrics (fingerprint) and the knowledge factor (on-device PIN code, 4 to 8 digits). Repeated failed PIN or fingerprint attempts are rate-limited on the device with an exponential back-off.
Future versions of CB may support additional static (face) and behavioral biometrics with dynamic characteristics such as the user's gestures, body motions, and voice*. Processing of biometrics and PIN verification takes place on the device and within a secure environment of the authenticator, without dependence on external resources or connectivity.
On-Body Detection & Gestures
The embedded motion sensor (6-axis IMU) lets the Badge recognise a double tap as confirmation of the user's intent to access a nearby device/desktop/IoT, if this is preferred to pressing a button or touching the fingerprint sensor. After a successful fingerprint verification the Badge keeps the user verified for an administrator-defined period (the user-verification cache, 4 hours by default), so subsequent logins need only a simple confirmation.
On-body detection - keeping the user logged into the authenticator while it is worn and logging out when no motion is detected for a configurable period - is supported by the sensor hardware and is being finalised in firmware*.
Presence based Login & Logout
When enabled, Crayonic Badge smart authenticator allows automatic login and logout via a specifically designed Bluetooth-USB dongle called Crayonic Bridge (CBLE) or via compatible NFC/BLE readers (e.g., mobile NFC rfIDEAS).
The Bridge requires no additional software or drivers installed on the endpoint devices. It serves as a "virtual cable" connecting the end point with Crayonic authenticators over a secured factory pre-paired Bluetooth protocol.
Remote or On-Premises Secure Access
Being compatible with multiple existing standards, communication channels, and operating systems, the Crayonic Badge can enable access to enterprise resources on-premises (e.g., desktop login) or remotely (e.g., RDP remote desktop, VPN, cloud services).
Legacy Application Authentication*
Crayonic Badge can act as a decentralized password manager that can autofill usernames and passwords for legacy Windows applications. For this functionality, a Crayonic Agent needs to be installed on an endpoint PC.
*This feature is planned and its availability depends on customer demand; contact Crayonic for the current status.
Configuration & Manageability
Crayonic Badges can be managed and configured using Crayonic Device Manager for fleet monitoring and Crayonic Credential Manager for passkey and certificate provisioning. Both rely on the Crayonic Agent middleware installed on MS Windows endpoints.
Indoor RTLS, Tracking, Panic Button
Besides identity and authentication use cases, the Crayonic Badge is a BLE beacon that on-premises positioning systems can locate. Crayonic RTLS (beta) uses these beacons - received by the Crayonic Bridges on workstations and, where needed, by Wi-Fi access points with a BLE gateway - to show where a badge is on a floor plan. Its headline use is the badge's panic button: one press and security sees the location of the badge and who is nearest (beta - see the RTLS page for status). Future firmware updates may also support the Android Find My Device network*.
Critical Notifications, Paging and Calendar Events
The Crayonic Badge can receive secure messages over BLE and show them on its e-paper display, with acknowledgement sent back to the sender. Crayonic Comms (beta) integrates this with enterprise paging, notifications (mail/calendar, nurse-call, lab-result and alarm systems) so that staff can be reached without a phone.
Secure Audio: Encrypted Recording for AI Transcription
The Badge has a built-in microphone and can record audio notes, dictation or a consultation directly on the device (up to 5 minutes per recording). Recordings are encrypted on the badge before they are written to storage, with keys derived from the badge's own FIDO2 credential - the same hmac-secret / WebAuthn PRF primitive the badge already uses for passkeys. Only the person holding that badge can later decrypt the recording, in the browser, by using the badge as their security key. Neither the transport nor the server ever holds a key that can decrypt a recording.
Encrypted recordings can leave the badge in two ways:
- over USB mass storage - the badge exposes an encrypted volume and the recordings are picked up from a workstation (with the Crayonic Bridge and Crayonic Agent this can be automated), or
- over Bluetooth to the Crayonic Mobile ID Wallet on the user's Android phone, which acts as a blind courier: it uploads the ciphertext and hands the service's signed receipt back to the badge so the badge can free the space (designed feature, see the Mobile ID Wallet page).
Transcription and delivery into your EHR are handled by the Crayonic Secure Audio Service; see Solution Architecture, Option 4 for the end-to-end flow.
Core Specifications - Crayonic Badge™
| Logical Access | FIDO2 & PIV over USB, BLE, NFC, Crayonic Bridge BLE (CBLE) |
| Physical Access | (Optional) (LF) 125kHz Proxcard, (HF) MIFARE Desfire, NTAG |
| Biometric verification factors | Fingerprint (up to 15 templates), FAR < 1:50 000 , FRR < 1:20 , Matching speed <300ms |
| Additional verification factors | On-device PIN (4 to 8 digits) |
| Protection mechanisms | Secure Element for cryptographic operations; Key storage; Trust root and certified TRNG. Certified against Common Criteria EAL5+ profile. Configurable on-device security policies. |
| Key management features | FIDO resident key management with master entropy secure recovery; (Optional) PIV key and X.509 certificate issuance; Key/value storage; |
| Cryptographic algorithms | ECDSA P-256, SHA-1, SHA-2, AES-256, HMAC, RSA 2048 |
| Secure display (Legacy B1 & B2) | 128x32 px OLED |
| Secure Touch e-ink (B3 & B4 & B5) | 264x176 px e-ink 2.7 inch with capacitive touch and Gorilla glass cover |
| Visual feedback | Orange LED |
| Audio Input/Output | Digital (PDM) microphone - 12.5 kHz 16-bit mono recording, encrypted on-device / Beeper |
| Mechanical protection | Medical grade plastic body with IP64 rating |
| Sanitization | Healthcare disinfectants, UV light and cleaning agents (alcohol, chloride) compatible |
| Temperature ranges | Operation: 0 °C to 45 °C, Storage: -10 °C to 55 °C |
| Battery | Rechargeable LiPo min. 400 mAh. Average expected duration - up to 1 month of standard use per charge. |
| Communication interfaces | NFC - ISO 14443; USB - ISO 7816/CCID, BLE 5.1 |
| Physical Card Interfaces (B2/B4) | Contact smart card reader (ISO/IEC 7816-1:2011) - connects card to nearby device over CCID standard protocol |
| Physical Card Embedded (B3 QES) | (Option) Embedded Thales IDPRIME 940 for QES or any other mFF form factor card with 10k MOQ |
| Motion sensor | 6-axis IMU for double-tap gesture and on-body detection |
| Mass Storage | AES (XTS) encrypted FAT volume, approx. 30 MB on the standard 32 MB flash (larger per request), for encrypted audio recordings or small documents |
| Manufacturing standards | Auditable secure manufacturing in the European Union (Slovakia); RoHS |
| Certifications | FIDO2 Level 1, Microsoft Entra ID, Secure Element Common Criteria EAL5+, CE |
| Dimensions | 96 mm x 61 mm x 7 mm(45g) |
See also Crayonic KeyVault Technical & Security Whitepaper
Authentication Use Cases Compatibility Table
| Use Case | Support | Connectivity |
| Badge personalization | ||
| Fingerprint, PIN code authentication | on-device | - |
| Gesture | on-device | - |
| Badge settings & security policies | on-device, Crayonic Credential Manager, Mobile ID Wallet | |
| Passwordless biometric login | ||
| to a PC over FIDO2, U2F | Windows 10 1903+ with MS Azure AD/hybrid | USB, BLE, NFC, CBLE |
| to a PC over PIV (X.509) | Windows 7+, Linux*, Mac OS 10.12+ | USB, NFC, CBLE(Windows) |
| to a web service over FIDO2 | Windows 10 1903+ (Edge, Chrome, Firefox, Brave) | USB, BLE, NFC, CBLE |
| Linux, Mac OS, ChromeOS | USB, CBLE | |
| iOS Safari | USB, NFC, CBLE* | |
| to a web service over U2F | Android | USB, BLE, NFC, CBLE* |
| to a web service with X.509 client certificate over PIV | Windows 7+, Windows 10 (Edge, Chrome, Brave) | USB, NFC |
| FIDO2 credentials backup & recovery via Crayonic Credential Manager | Windows 10+, Linux, Mac OS | USB |
| Certificate issuance (X.509) | ||
| Locally | Windows 7+ using the Crayonic PIV Manager app | USB |
| Remotely over FIDO2 via Crayonic Credential Manager | Windows 10+, Linux, Mac OS 10.12+ | USB |
| Mass storage | ||
| AES encrypted (approx. 30MB) FAT32 | Windows 7+, Linux, Mac OS 10.12+ | USB |
| Secure audio recording | ||
| Encrypted recording bound to the badge's FIDO2 credential | on-device; retrieval via Secure Audio Service | USB (mass storage), BLE (Mobile ID Wallet*) |
| Digital signing | ||
| Using internal X.509 certificate over CCID | Windows 7+, Linux, Mac OS | USB, NFC, CBLE |
| Using external card X.509 certificate over CCID | Windows 7+, Linux, Mac OS | USB, CBLE |
| Physical Access | ||
| ISO 14443 standard | N/A | NFC |
| RFID(125kHz), MIFARE DESFire protocols | N/A | NFC |
| OTP (per request TOTP, HOTP...)* | on-device | stand-alone, USB |
* Planned functionality; availability depends on demand and firmware release - contact Crayonic for the current status.